Start
Credentials map
One table for “what do I paste where?” — Admin login, Agent Protocol clients, runners, and connector secrets are different trust domains.
| Credential | Where it lives | Who uses it | Admin login? |
|---|---|---|---|
API key with admin | auth.keys in langgraph.json / Helm | Operators, curl to /admin-api | Yes |
auth.admin_keys | Same config object | Break-glass Admin only | Yes (Admin only) |
| API key read/write | auth.keys | App backends (Agent Protocol) | No |
JWT with admin claim | Your IdP | SSO operators | Yes |
RUNNER_TOKEN_* | Env on control plane + runners | Runner ↔ plane gRPC/HTTP | No |
RUNNER_TENANTS_* | Env on control plane | Tenant allow-list per runner kind | No |
Connector ${ENV} / secret_ref | Secrets / env / Vault | Plane vends run-bound sessions | No |
| Postgres / Redis URLs | Env / Secret | Control plane process | No |
How to implement (Supported)
- Mint a long random operator key; put it in a secret store; reference via env substitution in config if you use
${VAR}. - Put
adminon that key (or useadmin_keys). - Issue separate read/write keys per app / tenant — never share the Admin key with product backends.
- Set runner tokens per kind; when client auth is on, also set
RUNNER_TENANTS_*(fail-closed otherwise). - Keep connector secrets out of git; use
${NAME}orauth.secret_refin connector YAML (see Secrets).
In the product
Admin is an ops console — it does not mint or list API keys
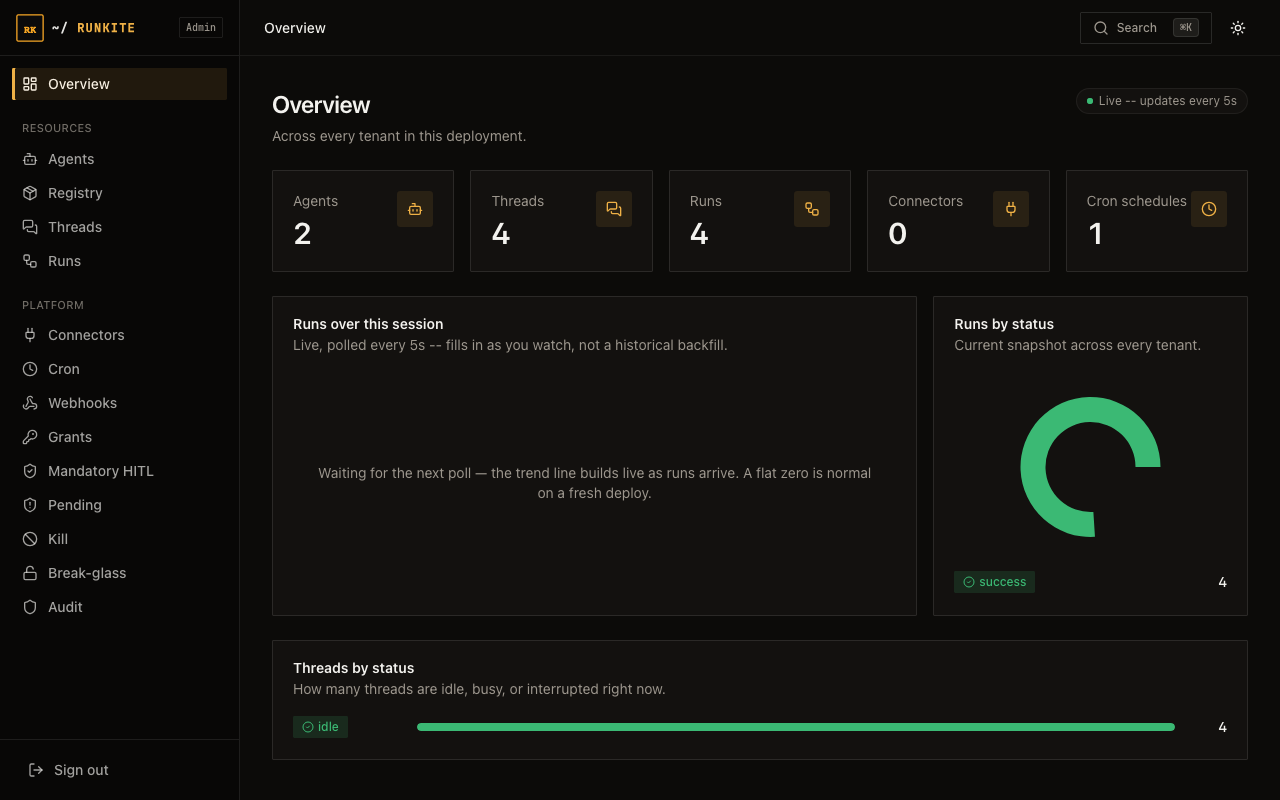
What to expect
- Rotating Admin — deploy new key in config/secret, restart/reload plane, update operator vault, revoke old.
- Leaked read/write key — can create runs in its tenant; cannot open Admin if it lacks
admin. - Leaked runner token — can pull jobs for allowed kinds/tenants; still not Admin.
Reference: docs/auth.md · Admin login · Security